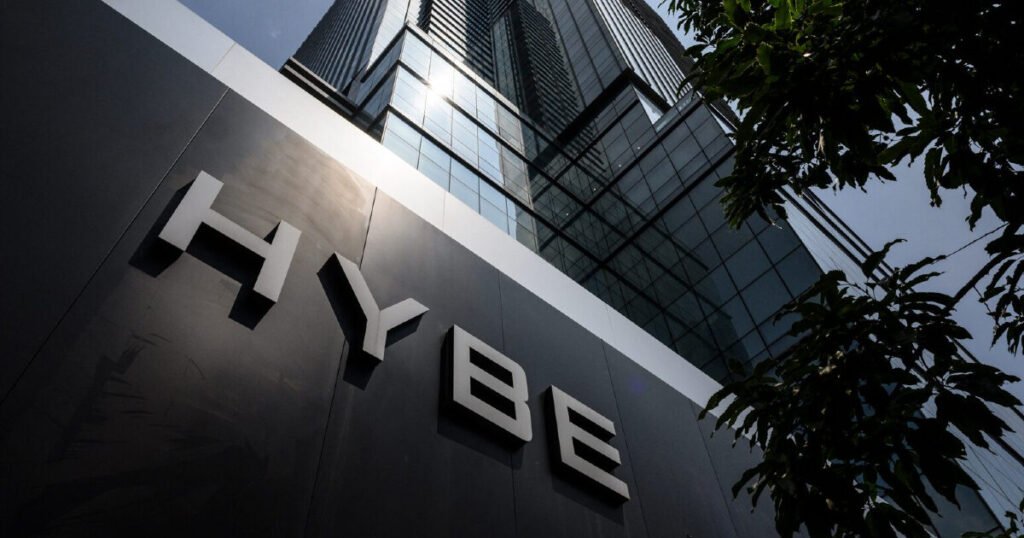
A massive personal information leak has occurred at HYBE, South Korea’s largest entertainment company, due to an external hacking attack.
The leaked information includes not only names and contact details but also extremely sensitive data such as resident registration numbers, passport numbers, account numbers, card numbers, and medical information.
HYBE recently issued an official apology, announcing that during an internal security inspection, abnormal external access was detected in an external vendor’s document preview solution linked to the electronic approval system. Further investigation revealed a similar unauthorized intrusion into the internal expense processing system.
As a result, some internal documents stored on the two system servers, including personal information contained within them, were leaked externally. The victims include partners of HYBE and some current and former employees.
HYBE reported that the leaks occurred in two incidents. The first leak took place from 1:16 p.m. on September 12 to 11:14 a.m. the following day, September 13. The second leak occurred from 10:41 p.m. on October 3 to 3:05 p.m. on October 5.
Leaked personal information includes names, resident registration numbers, foreigner registration numbers, passport numbers, account numbers, card numbers, mobile phone numbers, general telephone numbers, email addresses, home addresses, medical information, and dates of birth.
The exact leaked items vary depending on individual work and approval records; some affected individuals also had automatically generated information exposed, such as IP addresses, employee numbers, and department names.
Following the incident, HYBE promptly blocked the IP addresses and access routes used in the attack, immediately suspended the problematic external document preview service, and implemented emergency security measures.
Additionally, they completed notification procedures with relevant authorities, including the Korea Internet & Security Agency (KISA) and the Personal Information Protection Commission, and are individually informing the affected parties.
HYBE urged, “Do not respond to any contacts impersonating the company or employees demanding account info, money, or sensitive materials, and refrain from opening email attachments or clicking URLs from unknown sources.”
Additionally, they vowed, “We will strengthen access control and monitoring systems within the company to prevent recurrence and devote all efforts to security.“